


If you use Brave browser, then you should grab the latest update immediately. The company has pushed out an emergency update for desktop users, updating the browser to version 1.99.56 to shut down a nasty security bug that hackers are already using in real-world attacks.
According to the official release notes, this build bumps the underlying engine to Chromium 157.0.8103.50. It comes just five days after Brave 1.99.55 brought back split-view dragging and fixed a scary Leo AI bug.
The main thing to know this time around is a vulnerability tracked as CVE-2026-125350. In simple terms, it’s a memory issue in the way the browser handles XML data. Visiting a malicious webpage could allow harmful code to run on your computer, so it’s worth being cautious about unfamiliar links.
Google actually patched this exact flaw on Monday after an anonymous researcher tipped them off on November 6, noting in their advisory that they are “aware that an exploit for CVE-2026-125350 exists in the wild.”
Because Brave runs on that same Chromium engine under the hood, the team had to rush out their own patch to keep its 130 million monthly active users from getting hit by the same attacks targeting standard Chrome users.
Posting about the rollout on X, the company told users that “Today’s browser update (v1.99.56) contains a fix for a Chromium vulnerability found to be exploited in the wild,” adding that you might have gotten the automatic patch already, or you can grab it manually through the About Brave menu.
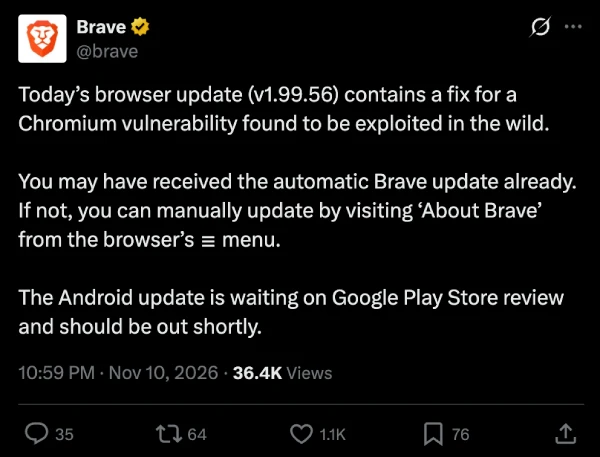
That said, the team says the patch for Android “is waiting on Google Play Store review and should be out shortly.” It’s still not live at the time of this writing on the Google Play Store. But we expect it to go live soon.
iPhone users who just got long-press link previews inside Leo AI answers do not have to sweat this specific bug at all. Apple forces every iOS browser to run on Safari’s WebKit engine rather than Chromium, so this particular flaw does not touch iPhones or iPads.

Dwayne Cubbins
3193 Posts
I cover fast-moving stories across apps, online platforms, and everyday tech — phones, wearables, consoles, and whatever else people are fighting with this week. Bugs, rollouts, scams, policy enforcement, and the occasional internet-culture rabbit hole are all fair game. My goal is simple — make confusing tech news readable. When I'm not working, I'm working out or chilling with my dog. Got a tip? You can find me on X @dcubbins.