


Mozilla just kicked out sixteen shady add-ons from the Firefox store after researchers found them quietly stealing crypto credentials. The trick? They looked like innocent desktop tools or straight-up clones of popular Web3 wallets like Rabby and OKX.
The security team at Socket, which spotted the scam, says these add-ons were built to grab your seed phrases and private keys the moment you tried to import a wallet.
And this isn’t a one-off headache. Back in August, we talked about dozens of rogue Firefox extensions quietly hijacking crypto keyrings and clipboard data. Researchers think this latest batch is from the same crew. They keep running the same scam because, well, it keeps working.
Four of the bigger add-ons were basically carbon copies of Rabby Wallet, just with sneaky typos like “Raabby WaIIet” to slip past review filters. The other twelve were smaller utilities pretending to be OKX or generic Web3 tools.
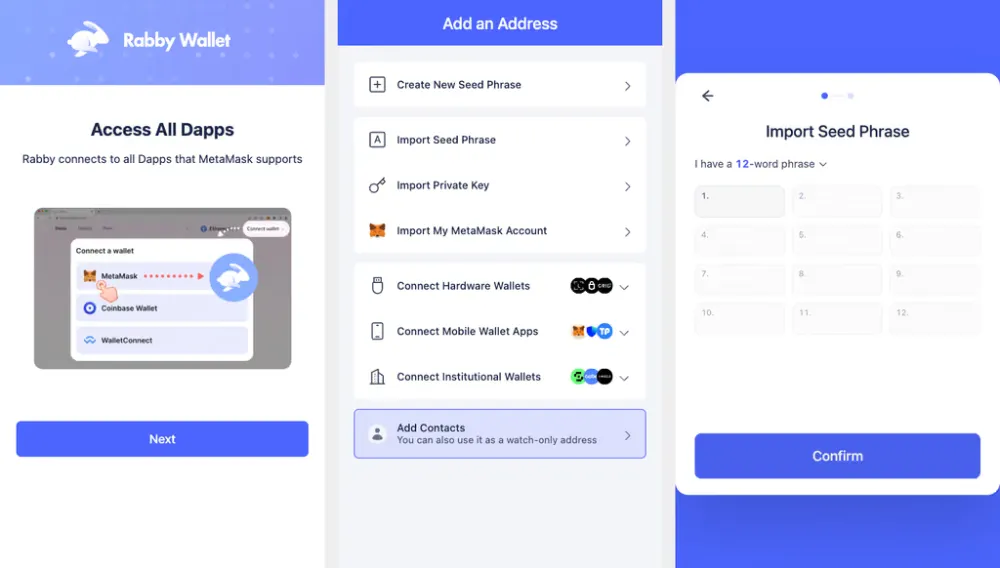
If you typed in your 12 or 24-word recovery phrase, the extension just grabbed the text and sent it straight to the attackers’ Cloudflare Workers.
That kind of bait-and-switch has become uncomfortably common lately. Just last month, another rogue add-on made the rounds disguised as a PDF helper while secretly trying to take over Google accounts. Bad actors know most people implicitly trust add-on storefronts, so getting a malicious package approved is half the battle.
Mozilla officially pulled all sixteen add-ons on October 5. But here’s the catch: deleting the add-on after the fact won’t magically save your crypto.
As Socket pointed out in their findings, “Changing only the extension password does not revoke a stolen seed phrase or private key.” If you typed your credentials into any of these extensions, the attacker already has the keys to your funds. The only real fix is setting up a fresh wallet on a clean device and transferring every asset out immediately.
Here are the 16 malicious extension IDs identified in the campaign. Check your browser add-ons manager and remove them immediately if you find any.
- [email protected]
- [email protected]
- [email protected]
- [email protected]
- [email protected]
- [email protected]
- [email protected]
- [email protected]
- [email protected]
- [email protected]
- [email protected]
- [email protected]
- [email protected]
- [email protected]
- [email protected]
- [email protected]

Dwayne Cubbins
3097 Posts
I cover fast-moving stories across apps, online platforms, and everyday tech — phones, wearables, consoles, and whatever else people are fighting with this week. Bugs, rollouts, scams, policy enforcement, and the occasional internet-culture rabbit hole are all fair game. My goal is simple — make confusing tech news readable. When I'm not working, I'm working out or chilling with my dog. Got a tip? You can find me on X @dcubbins.