


Google is rolling out a big security update for Chrome. It is rolling out as version 155.0.8059.39/.40 on Windows and Mac, alongside .39 for Linux, packing a huge list of 247 security fixes.
This follows the company’s announcement of the gradual rollout of Chrome 155 earlier this month. Back then, we didn’t have any official changelog or information about security fixes. Now, it’s clear that it’s a massive release, especially in terms of the number of vulnerabilities patched.
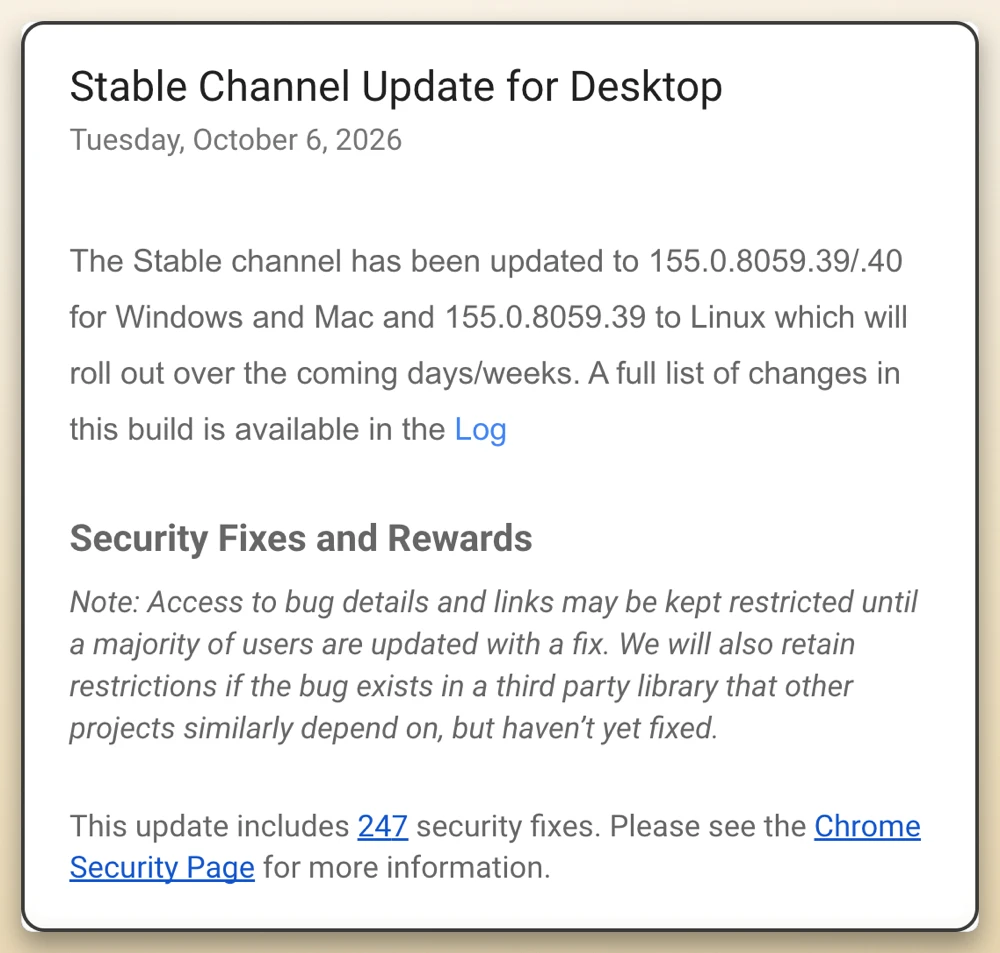
To put that number in perspective, this comes right after another release last week, when Google scrambled to shut down over 30 security threats. Seeing nearly 250 security bugs addressed in one fell swoop is wild, even for a browser with a codebase as massive as Chromium.
In its release notes, Google marked four of these flaws as critical. One was caught internally in Chromecast (CVE-2026-106382) and another in the browser core (CVE-2026-106197). The remaining two critical bugs came from Anthropic researcher Xinyang Ge, who was directly assisted by Claude.
Those two Claude-assisted criticals, tracked as CVE-2026-106358 in Navigation and CVE-2026-106347 in Track, are use-after-free bugs. To keep things simple, these memory flaws happen when a program gets confused about what data is still stored in RAM. Attackers love them because they can open the door to running malicious code right on your machine.
Anthropic did not stop there either. Xinyang Ge and Claude submitted ten more high-severity bugs across the PDF engine, WebRTC, and media components, including CVE-2026-106278, CVE-2026-106233, CVE-2026-106318, CVE-2026-106411, CVE-2026-106423, CVE-2026-106357, CVE-2026-106383, CVE-2026-106349, CVE-2026-106421, and CVE-2026-106204.
But Anthropic wasn’t the only one reporting bugs. OpenAI’s Codex Security team also reported two high-severity flaws, including a use-after-free issue in HTML (CVE-2026-106257) and a type confusion bug in the V8 engine (CVE-2026-106240).
As usual, Google is keeping details of these flaws under wraps until most users are on the latest version of Chrome. This keeps threat actors from reverse-engineering working exploits and targeting users who haven’t updated their browsers.
Speaking of updates, Google is also working on a smart idle restart system for Chrome that will wait for you to step away before restarting your browser after an update.

Dwayne Cubbins
3090 Posts
I cover fast-moving stories across apps, online platforms, and everyday tech — phones, wearables, consoles, and whatever else people are fighting with this week. Bugs, rollouts, scams, policy enforcement, and the occasional internet-culture rabbit hole are all fair game. My goal is simple — make confusing tech news readable. When I'm not working, I'm working out or chilling with my dog. Got a tip? You can find me on X @dcubbins.